How to Use Azure Managed Identity Effectively
What zero-trust Redis authentication does
Normal Redis authentication: you generate a token. Store it. Rotate every 90 days. Manage backups. Handle failures.
Zero-trust with Managed Identity: your app has an identity. Azure verifies your app. Returns a token. App uses it. Token expires, app requests a new one. No human involvement. No rotation schedule. No secrets stored.
How Azure Managed Identity works
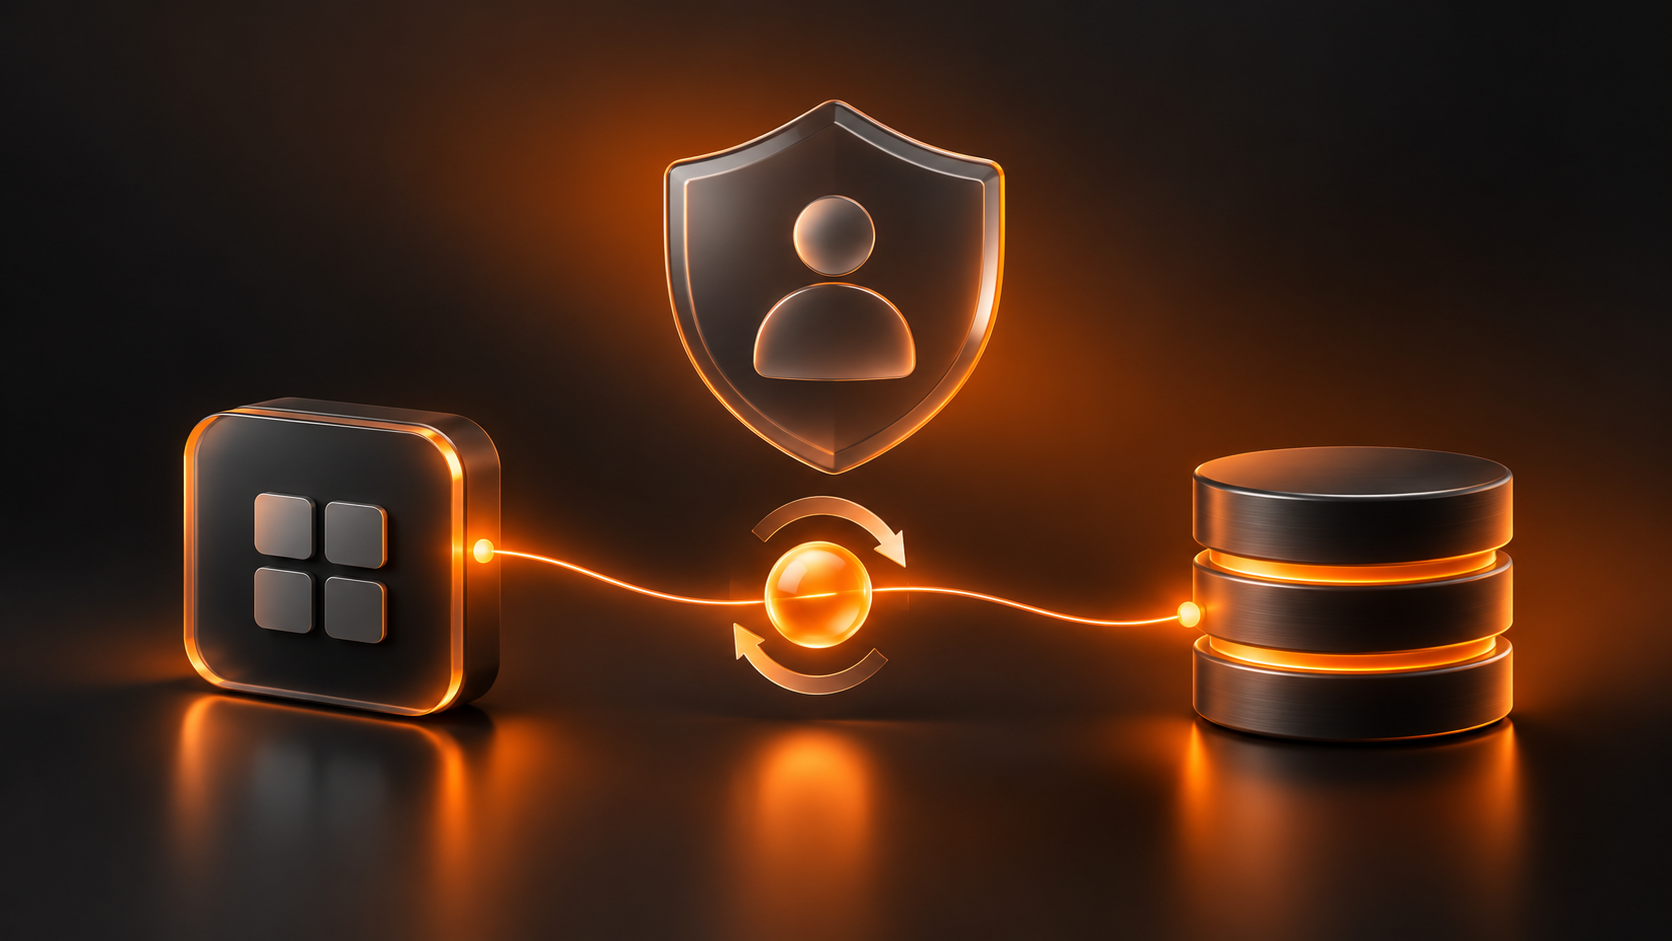
Azure Managed Identity assigns an identity to your application. Your app is an identity. Redis knows your identity.
Your app requests a token at runtime. Azure verifies. Returns token. App connects to Redis. Token expires, app requests new one. Automatic.
Step-by-step setup
Step 1: Enable Managed Identity
In Azure Portal:
Go to your App Service
Navigate to Settings > Identity
Toggle 'System assigned' to On
Azure creates an identity for your app
Step 2: Grant identity access to Redis
In Azure Portal:
Go to your Azure Cache for Redis
Navigate to Access Control (IAM)
Add role assignment
Role: Redis Cache Data Contributor
Assign to: Your app's managed identity
Step 3: Update your code
Old approach (with static secret):
const redis = require('redis');
const token = process.env.REDIS_TOKEN;
const client = redis.createClient({ host: 'myredis.redis.cache.windows.net', port: 6380, password: token, tls: true });
New approach (with Managed Identity):
const { DefaultAzureCredential } = require('@azure/identity');
async function getRedisToken() {
const credential = new DefaultAzureCredential();
const token = await credential.getToken('https://redis.azure.com');
return token.token;
}
const token = await getRedisToken();
const client = redis.createClient({ host: 'myredis.redis.cache.windows.net', port: 6380, password: token, tls: true });
Security benefits
No secrets in config files
No secrets in environment variables
No secret rotation complexity
No human access to secrets
No backup tokens
Zero static secrets anywhere. Try it on your projects - https://www.walnutai.ai/